Version 2026.3
Thank you for updating Remote Desktop Manager (RDM) to version 2026.3!
Below, we'll take a quick look at the most exciting updates. For the full list of changes, check out the release notes.
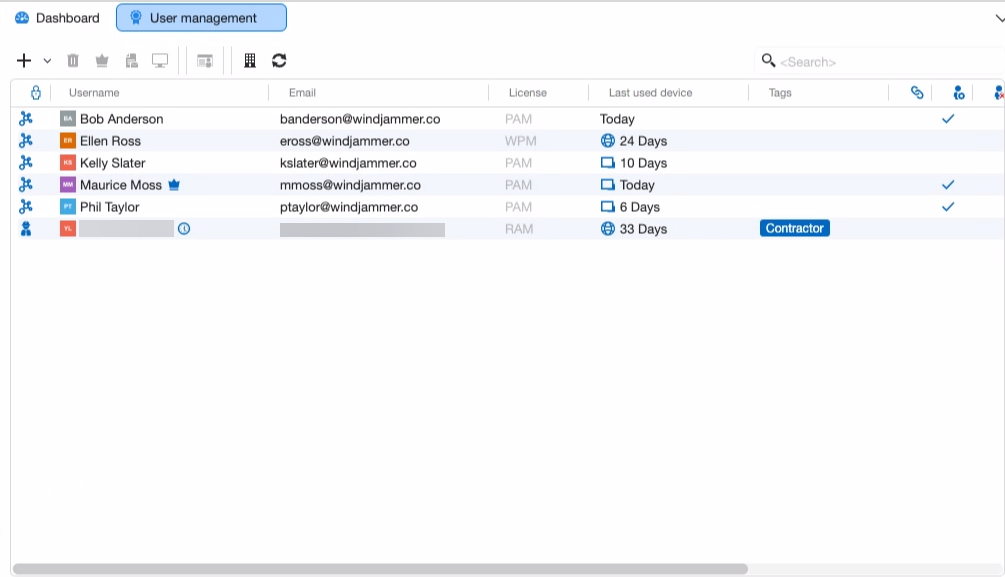
Manage Devolutions Cloud users in RDM
You can now manage Devolutions Cloud users in Devolutions Remote Desktop Manager (RDM), instead of the Devolutions Cloud web interface. You can search for and filter users, add users, administrators, or contractors, and send or resend invitations. You can also view licenses, user groups, registered devices, and user activity.
In RDM for macOS, open User management. You can also manage user groups there.
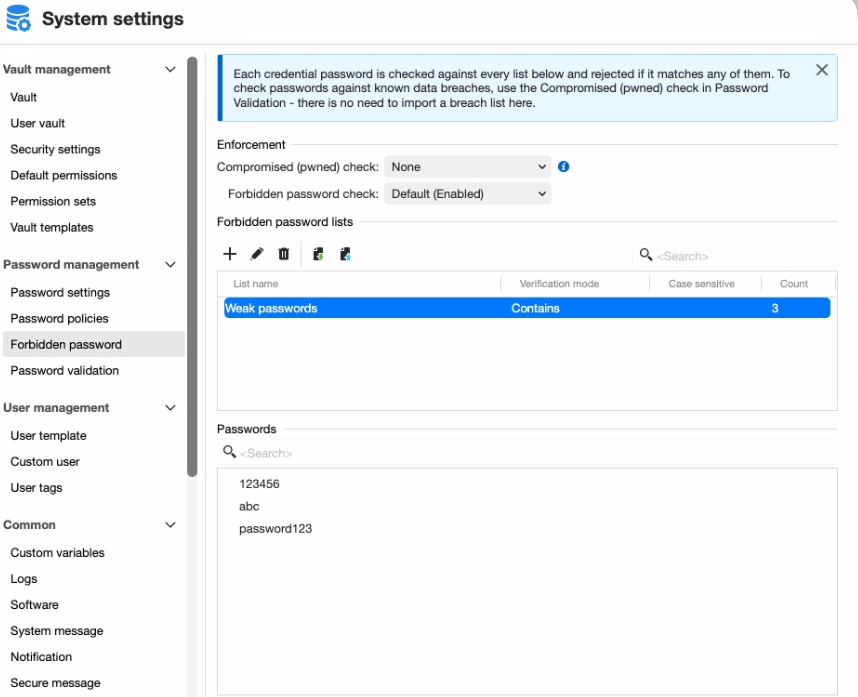
Manage Devolutions Cloud system settings in RDM
You can now manage the supported Devolutions Cloud system settings in RDM, instead of the Devolutions Cloud web interface. RDM could already manage system settings for SQL Server and Devolutions Server workspaces.
Store PAM credentials in shared vaults
You can now store Devolutions PAM credentials in a regular shared vault, alongside standard entries. A vault must be at the High security level before it can hold PAM accounts. A vault at Standard refuses a PAM entry and asks an administrator to convert the vault first. High-security vaults are not available offline, and a vault that holds PAM accounts cannot return to Standard until you move or delete those accounts.
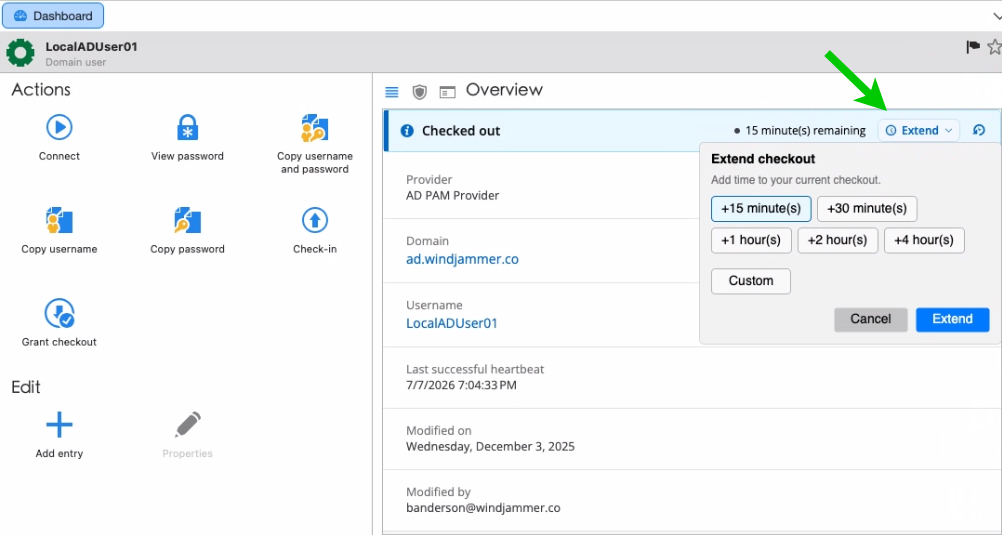
Extend active PAM checkouts
You can now request more time on an active PAM checkout, instead of checking the credential in and starting a new request. Extensions are off by default. The checkout policy controls whether extensions are available, whether approval is required, and the maximum extension duration.
Keep existing just-in-time PAM accounts between checkouts
The just-in-time (JIT) account mode now includes Enable account on checkout, alongside None and Create the account on checkout. The new mode allows an existing account to be used at checkout, instead of creating a new one. At check-in, it disables the account again.
At checkout, the server also applies the account's configured elevation-group membership and removes it at check-in. RDM for macOS shows the settings that the server controls.
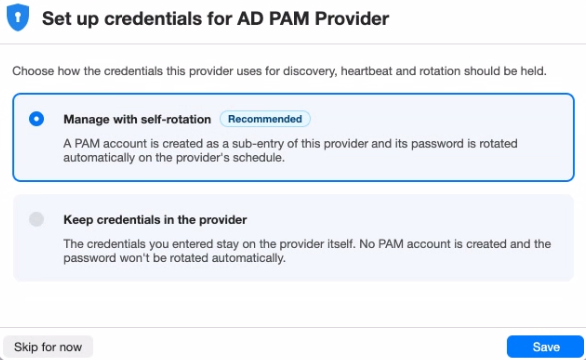
Manage PAM provider credentials with self-rotation
A PAM provider signs in with its own account to run discovery, heartbeat, and password rotation. When you save a provider, you can now choose Manage with self-rotation, Keep credentials in the provider, or Skip for now. You can also convert an existing provider to a Managed PAM account. The managed account appears under the provider and follows the provider's rotation schedule.
In RDM for macOS, use Convert to managed PAM account on an existing provider. It replaces the manual scan, import, and link sequence.
Discover PAM accounts with the RDM SQL Server data source
For an RDM SQL Server data source, Account Discovery Preview shows the accounts a scan would discover, along with their risk signals. Any RDM user can run the preview, and you do not need a PAM license to view the results. The preview is read-only: results stay in memory for the session and are cleared when the window closes. Acting on what you find, including import, export, scheduling, and account management, requires a PAM license.
Create a vault from a template
When you create a vault, you can select a vault template to copy its folders and entries with their nesting. In RDM for macOS, templates are available when you create a vault for a Devolutions Server workspace.
Create multiple forbidden password lists
Each list has its own match mode (Exact or Contains) and its own case-sensitivity setting. With the Forbidden password check on, a password that matches any list is refused before you save it.
In RDM for macOS, you can create these lists for local and supported workspaces. The rules apply during password validation.